Which of the following is not a method of purging that uses dedicated, standardized device sanitize commands that apply media-specific techniques to bypass the abstraction inherent in typical read and write command? (Wentz QOTD) A. Overwrite B. Block erase C. Degaussing D. Cryptographic Erase
Your organization initiated an outsourcing project to develop the customer relationship management (CRM) system that would operate on a PaaS from a public cloud service provider. Mobile devices as CRM clients are purchased from a well-known brand. As a project manager, which of the following is the least concern in terms of procurement? (Wentz QOTD) A. System and Organization Controls (SOC) B. Capability Maturity Model Integration (CMMI) C. Trusted Computer System Evaluation Criteria (TCSEC) D. CISSP (Certified Information Systems Security Professional)
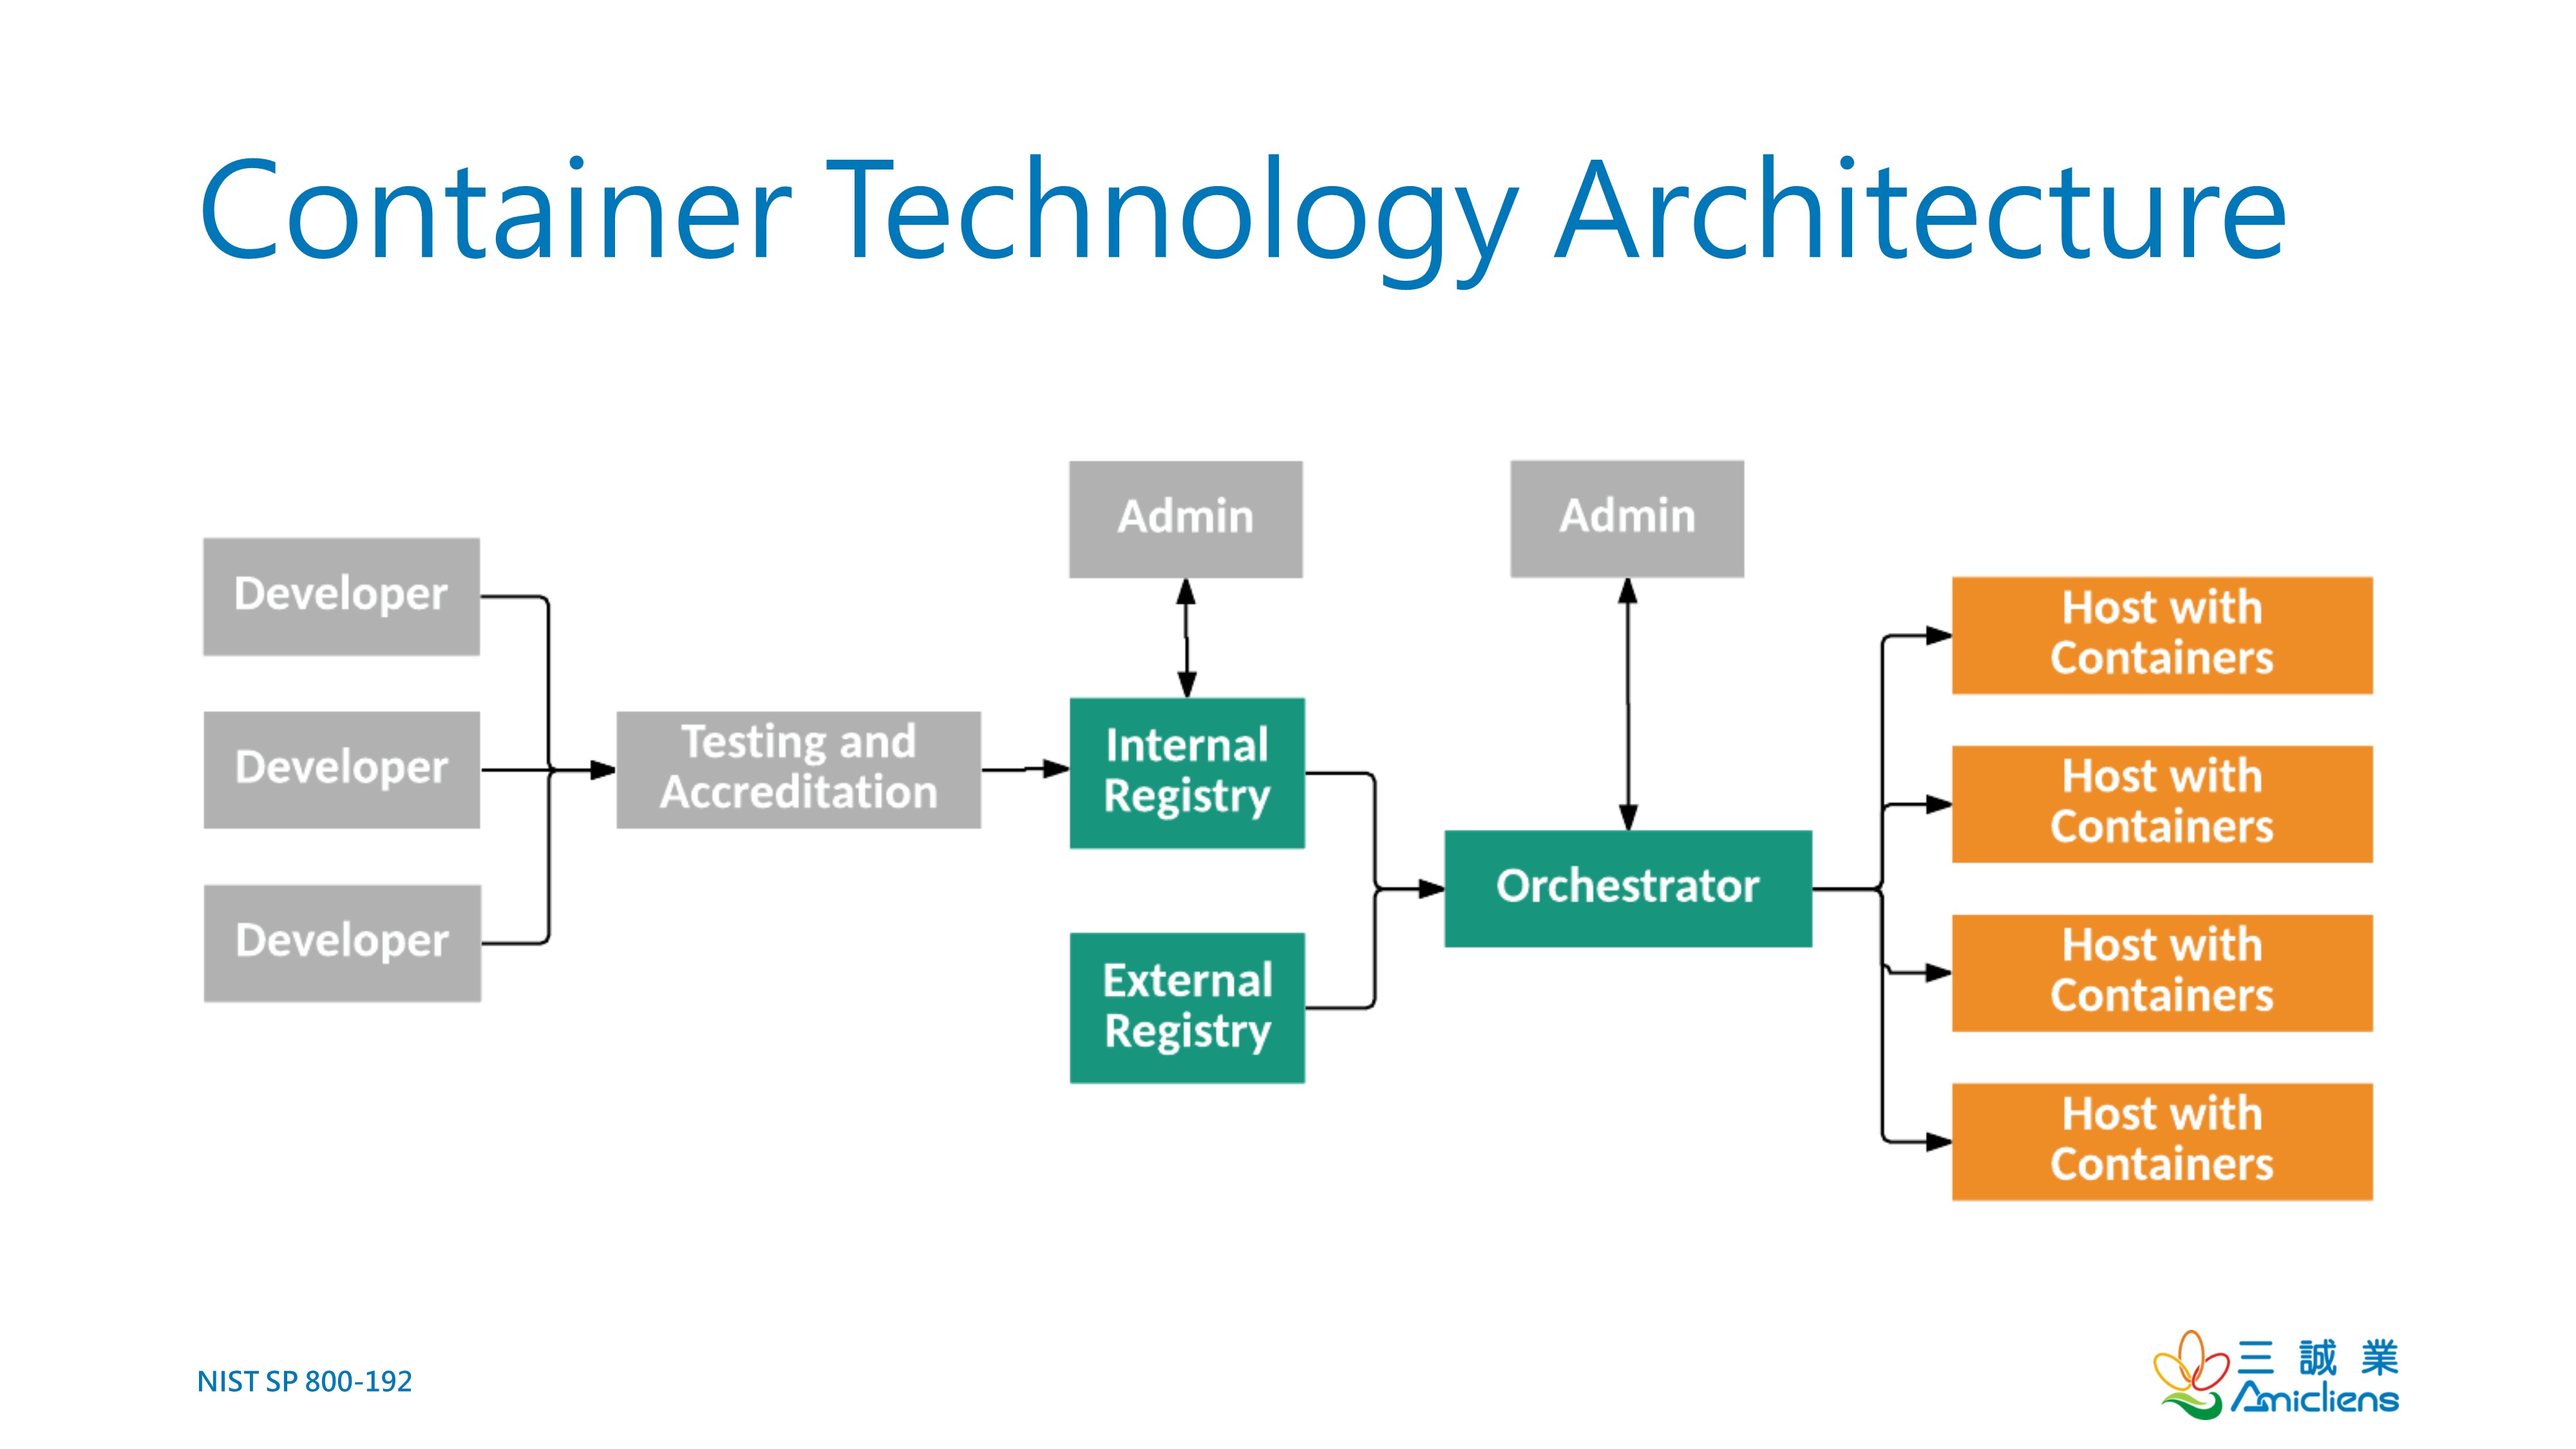
A container image is a package created and registered by developers that contains all the files, typically organized in layers, required to run in a container. An image typically comprises layers, such as the minimum OS core (aka base layer), application frameworks, and custom code.
Even though a host could directly contact a registry for an image and deploy it into a container, orchestrators such as Kubernetes (K8S), Docker Swarm, Mesos, etc., can automate the deployment process to pull images from registries, deploy them into containers, and manage the container runtimes.
As a CISO, you frequently travel on business and connect to corporate mail servers through VPN for security. You’d like to send a strategic plan to the CEO from a luxury five-star hotel remotely. Which of the following best ensures non-repudiation of the email? (Wentz QOTD) A. Asymmetric encryption using key pairs B. Elliptic Curve Digital Signature Algorithm (ECDSA) C. IPsec in transport mode using AH and certificates D. IPsec in tunnel mode using ESP and shared secrets
This book is not a CISSP study guide but one that helps you lay a solid foundation of security governance and risk management. You will find it helpful in your CISSP and CISM journey!
Yes, both CISSP and CISM!
Buy it on Amazon: https://www.amazon.com/dp/B087JL6BXR I’d love to see your kind comment on my book on Amazon! Thank you so much for your attention!
Which of the following best aligns with the security principles of containerization? (Wentz QOTD) A. Overlay networks are commonly used to monitor traffic between nodes. B. Containers shall be deployed on the same host to impose the security baseline. C. Containers are stateless and immutable, against which in-place patches are not allowed. D. General-purpose OSs are more flexible and suitable for reducing attack surfaces of containers.
Which of the following least aligns with the concept of Zero Trust? (Wentz QOTD) A. Record network traffic for visibility B. Encrypt traffic over LAN using IPSec C. Dynamically open ports using port knocking D. Implement multi-tier firewalls as part of the defense-in-depth strategy
Your organization implemented an anomaly-based Intrusion Detection System (IDS) designed to optimize false-negative probability and minimize potential losses. However, the IDS triggered too many false alarms. As the IDS administrator, you are evaluating the configuration change to reduce the number of false alarms. Which of the following is the least likelyramification of the change? (Wentz QOTD) A. Zero-day exploits might increase B. Investigation workload might decrease C. The sensitivity of the IDS might be lowered D. The detection threshold of IDS might be enlarged
A tunnel is a logical link or point-to-point connection, established through tunneling protocols, that encapsulates payloads between two nodes over a public or shared network. Still, other security services or protocols protect data transmitted through the tunnel. Which of the following is not a tunneling protocol? (Wentz QOTD) A. Virtual Extensible LAN (VXLAN) B. Layer 2 Forwarding Protocol (L2F) C. Generic Routing Encapsulation (GRE) D. Encapsulating Security Payload (ESP)
I came across this post about the brute force attack in Luke’s group and respectfully disagree with the suggested answer “C. using a rainbow table to compare known hashes to unknown hashes.” Instead, I suggest option “D. repeatedly guessing a user’s password until the correct one is found” BEST describes a brute-force attack.